CVE-2026-86206, CVE-2026-86207: N-able N-central Authentication Bypass (FIXED)
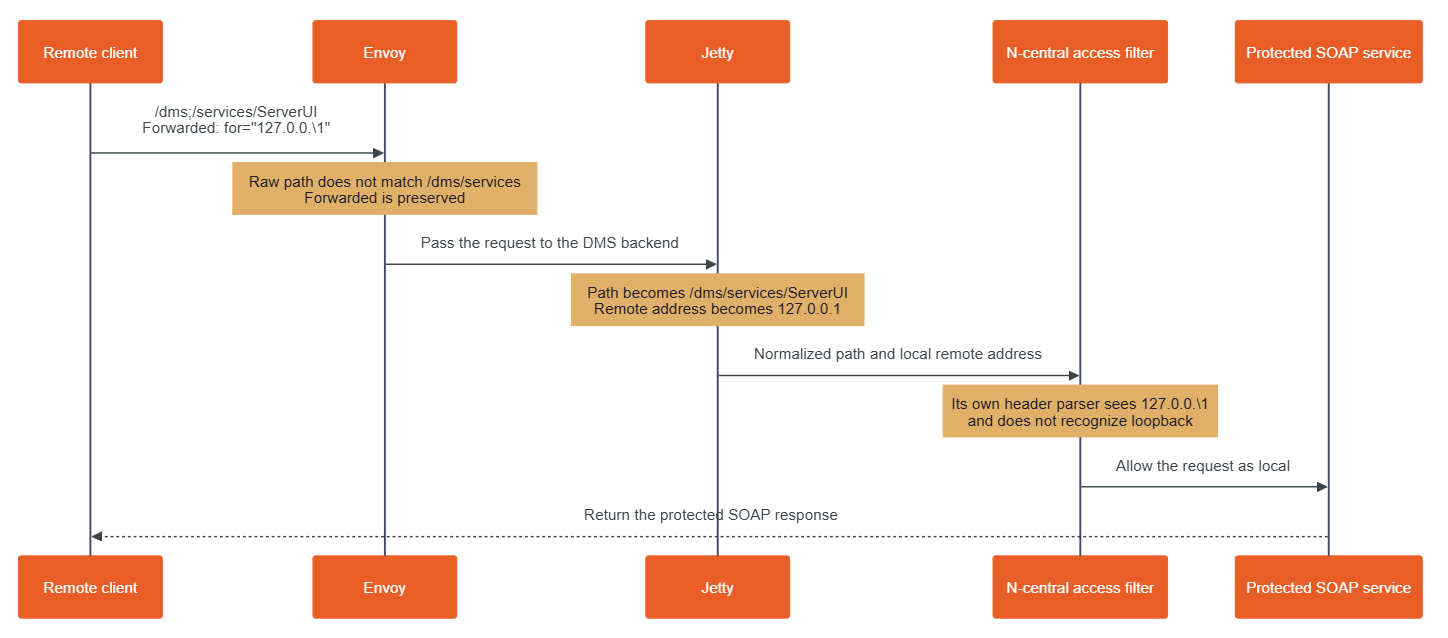
OverviewWhile conducting research into a recent N-able N-central authentication bypass vulnerability (CVE-2026-18577), Rapid7 Labs discovered two new vulnerabilities affecting the latest version of N-central. When chained together, these two vulnerabilities allow a remote unauthenticated attacker to bypass authentication and create a new attacker-controlled System administrator account on an affected server.CVE IDDescriptionCWECVSSv4CVE-2026-86206Semicolon/Forwarded access-control bypassCWE-7916.9 (Medium)CVE-2026-86207UserTwoFactorLogin authentication bypassCWE-3057.7 (High)Both CVE-2026-86206 and CVE-2026-86207 have been patched by the vendor via N-central 2026.3 Hotfix 3.Product descriptionN-able N-central is an enterprise-grade Remote Monitoring and Management (RMM) platform designed for Managed Service Providers (MSPs) and IT departments to monitor, manage, and secure complex, large-scale networks from a centralized dashboard.CreditThese vulnerabilities were discovered by Stephen Fewer, Senior Principal Security Researcher at Rapid7, and are being disclosed in accordance with Rapid7's vulnerability disclosure policy.Technical analysisCVE-2026-86206N-central exposes its manage…