rillr
About Guidelines Privacy Terms Log in Join Rillr
Rillr / Topic

Cybersecurity

Latest stories and discussion in Cybersecurity.

CISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code Execution

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday confirmed active exploitation of the recently patched PHP2Shell flaws by adding them to its Known Exploited Vulnerabilities (KEV) catalog. The PHP vulnerabilities, both rated 9.2 on the CVSS scoring system, facilitate unauthenticated remote code execution on affected deployments - CVE-2026-109618 - An out-of-memory

💬 0 ↗ source

Brotli2Shell: Frequently asked questions for Google Brotli decoder vulnerability (CVE-2026-111497)

Researchers have demonstrated remote code execution through CVE-2026-111497, an out-of-bounds write in Google's Brotli decoder library, and public proofs-of-concept (PoCs) are available. Software that uses the decoder includes Node.js, .NET, Bun, Envoy Proxy, Istio, Python HTTP clients and PHP for Windows.Key TakeawaysCVE-2026-111497, known as Brotli2Shell and by several other names, is an out-of-bounds write in Google's Brotli decoder library that Google, the CVE Numbering Authority (CNA), scored 9.2 under CVSSv4.0.Any application that decompresses attacker-controlled data with a vulnerable Brotli decoder is potentially at risk, including Node.js, .NET, Bun, Envoy Proxy, Istio, Python HTTP clients, FFmpeg, Apache Arrow and ClickHouse.Patches are available for Google Brotli and the major runtimes, though some projects had not shipped a fixed release as of October 26, and applications that bundle their own copy of Brotli each need their own fix.BackgroundTenable's Research Special Operations (RSO) team has compiled this blog to answer Frequently Asked Questions (FAQ) regarding Brotli2Shell, a vulnerability in Google's Brotli C decoder library, which Node.js, .NET and other software…

💬 0 ↗ source

Women's jobs show greater vulnerability to AI than men's

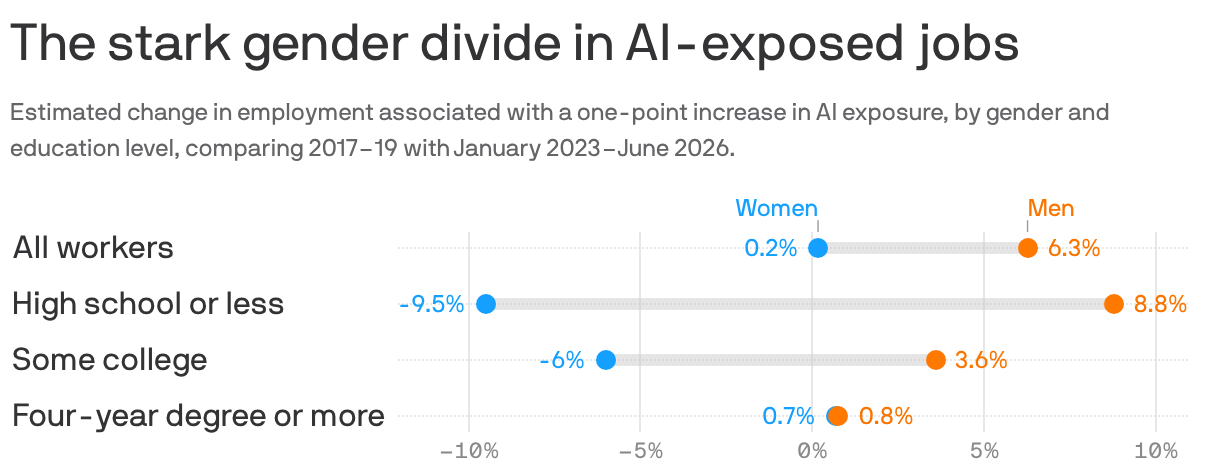
Data: Pew Research Center. Chart: David Adkins/Axios Women without four-year degrees are losing ground in jobs with more exposure to AI, while men with similar education levels are seeing employment gains, according to a new Pew analysis.Why it matters: Women could be exposed to greater economic disruption than men as AI reshapes the workplace.The big picture: For workers without four-year degrees, the gap in employment growth between men and women widened as AI exposure increased, Pew found.High school diploma or less: For each one-point increase in AI exposure, men's employment grew 8.8%, compared with a 9.5% decline for women.Some college, including associate degrees: Men's employment grew 3.6%, while women's declined 6%.Bachelor's degree or higher: Neither group saw a significant change.What's happening: Men and women without four-year degrees tend to work in different occupations, leaving them with different levels of AI exposure.Men without four-year degrees are more concentrated in jobs with low AI exposure, including truck driving, construction and freight moving. Their employment gains in highly exposed jobs apply to a relatively small share of men without bachelor's degr…

💬 0 ↗ source

Discover and remediate PHP2Shell exposure with Tenable

Learn how to use Tenable solutions to find vulnerable PHP versions, prioritize remediation, and patch the critical PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) faster.Key takeawaysThe PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) put security teams in a race against attackers. PHP runs on more than 70% of websites, so organizations need to quickly find where they’re affected and update PHP to fixed versions.Tenable helps you find PHP2Shell across your attack surface. Tenable One Attack Surface Management discovers externally facing PHP assets. Tenable One Vulnerability Management and Tenable Security Center provide detections, including local checks for Linux distribution packages. Tenable One Web App Scanning assesses web applications, and Tenable One Cloud Exposure covers cloud workloads.Tenable accelerates remediation. Tenable Patch Management matches exposures to the right patches, launches patch workflows, and validates fixes with post-scan checks. Tenable One with Tenable Hexa AI lets you find vulnerable assets, create exposure initiatives, and generate remediation tickets with simple prompts.Respond faster with Tenable solutionsThe recen…

💬 0 ↗ source

Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento

An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025. According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece of code to the store's pages that, when visited by unsuspecting users, serves malicious JavaScript loader code through Magento CMS blocks. "When you

💬 0 ↗ source

Solana Trading Bot Hacked for Nearly $1M, 49 Wallets Drained

Bloom Trading lost nearly $1 million in a security breach that drained 49 cryptocurrency wallets belonging to just nine users. The attacker exploited a software vulnerability, yet the company insists no private keys were stolen and promises full reimbursement. Hacker Drains 9,408 SOL Through Third-Party Vulnerability Bloom, a Telegram-based cryptocurrency trading bot supporting Solana and […]

💬 0 ↗ source

PHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution Flaw

PHP has rebuilt its official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a flaw in the Brotli compression library that the packages include. The flaw can let an attacker corrupt memory and potentially run code. PHP says the flaw can be reached through the cURL extension when the extension decompresses HTTP responses automatically. cURL leaves that off by default, but

💬 0 ↗ source

Metabolic vulnerability identified in small cell lung cancer

Researchers at the University of Cologne have demonstrated that, while various cellular states of small cell lung cancer are equally dependent on the amino acid cysteine, they react differently when deprived of it. While some cancer cells subsequently die via ferroptosis—a form of cell death in which harmful oxidized fats accumulate in the cell membranes—others undergo apoptosis, a controlled, programmed form of cell death.

💬 0 ↗ source

Attackers Use Microsoft Teams IT Support Scams to Deploy Malware and Ransomware

Cybersecurity researchers are calling attention to what they say is a "recurring social engineering pattern" across hundreds of cases in which threat actors use Microsoft Teams' external chat creation feature to conduct impersonation scams or to deliver malware. "A consistent pattern of attacker behavior has emerged across these incidents: the use of the same throwaway tenants, the same 'IT

💬 0 ↗ source
Loading more stories…